Applicable products
- QNAP NAS running Plex Media Server 1.43.2 or earlier.
Overview
Plex2Shell refers to four vulnerabilities in the third-party application Plex Media Server, affecting version 1.43.2 and earlier: CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656. Each presents limited risk on its own, but chained together they allow an unauthenticated remote attacker to execute arbitrary code with the privileges of the Plex Media Server process.
According to Plex, a public proof of concept was released on October 16, and internet-facing servers that have not been updated have since been subject to widespread attacks. Compromised servers have been used to run cryptocurrency miners and proxy software.
The fixed release, Plex Media Server 1.43.3 (build 1.43.3.10861 and later), is available in the QNAP App Center. The vulnerabilities reside in Plex Media Server only; QNAP operating systems such as QTS and QuTS hero are not themselves affected.
Important: If Plex on your NAS was reachable from the Internet while running 1.43.2 or earlier, updating alone is not enough. Treat the NAS as potentially compromised and complete the clean reinstall, compromise check, and credential reset described below.
Q1. Is my NAS affected?
Only a NAS with Plex Media Server 1.43.2 or earlier installed is affected. QNAP operating systems are not themselves affected, and a NAS without Plex needs no action.
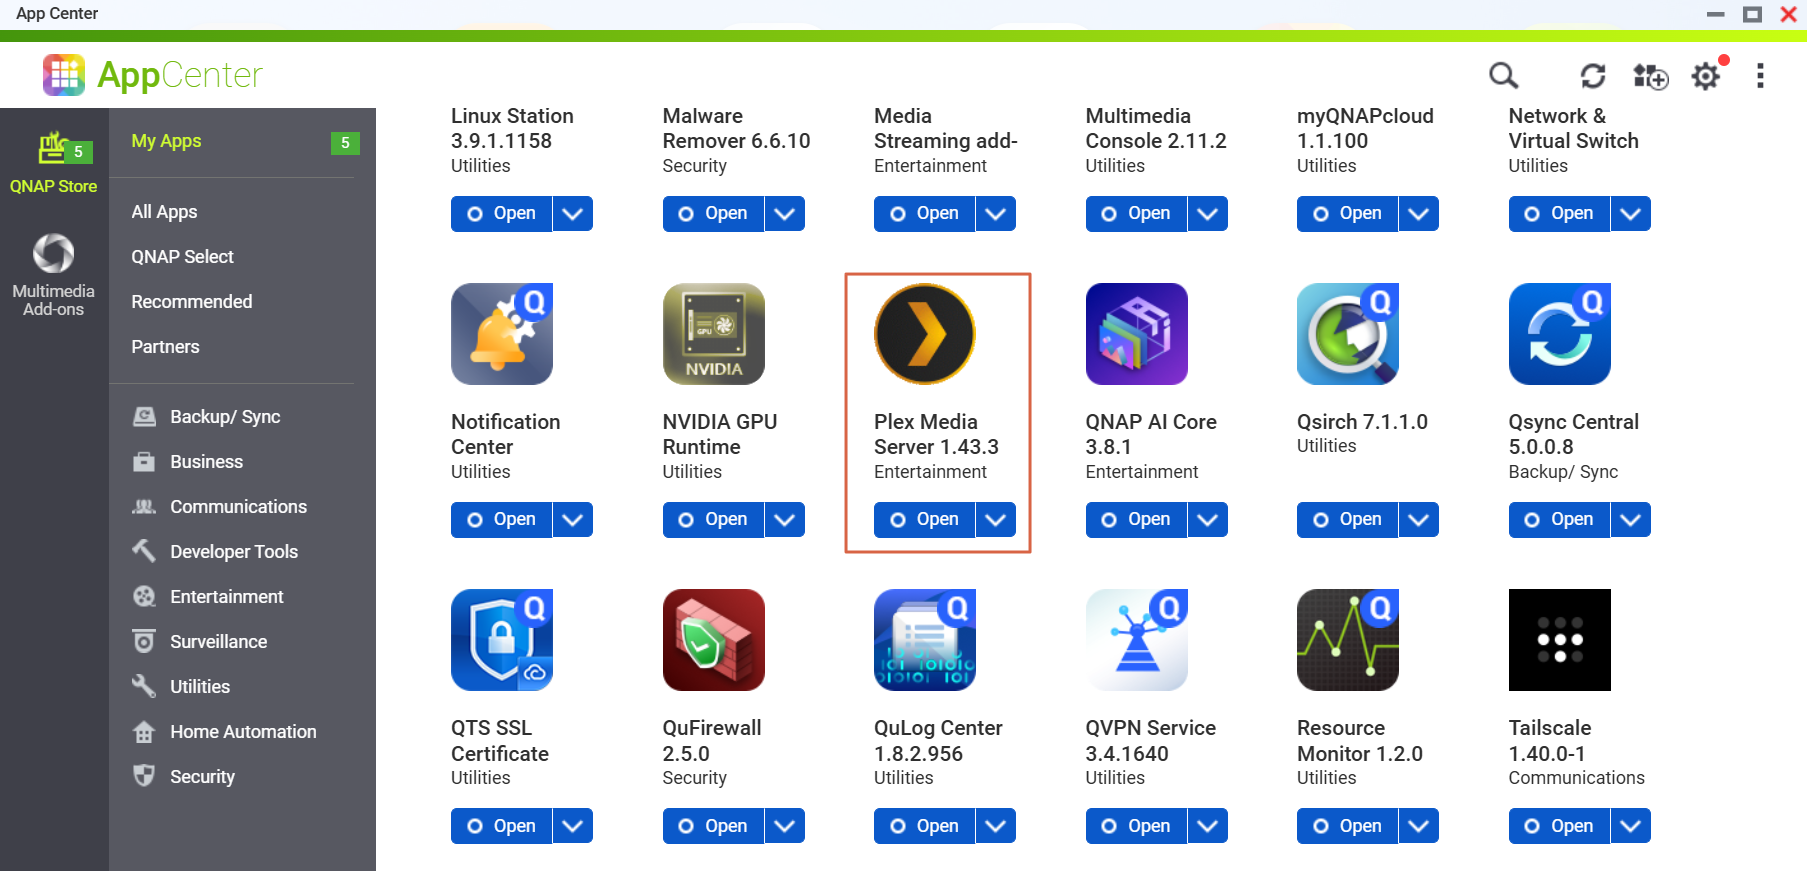
To check the version:
- App Center > My Apps shows 1.43.3 for the patched release.
Q2. How do I know whether my Plex was reachable from the Internet?
If any of the following applied while you were running 1.43.2 or earlier, or if you upgraded to a non-affected version only after the PoC was publicly disclosed on October 16, treat the NAS as potentially compromised and complete Q4 to Q8:
- Remote Access was enabled in Plex Web > Settings > Remote Access;
- your router forwards port 32400;
- UPnP is enabled on your router and Plex Remote Access was enabled (Plex opens the port automatically);
- Plex was exposed through myQNAPcloud auto router configuration or any other means.
Q3. How do I update?
- Go to App Center > My Apps > Plex Media Server > Update.
- Confirm that the version is 1.43.3. or later.
If no update is shown, refresh App Center and make sure the NAS can reach the Internet.
Later Plex releases (with other security fixes) will also be published once verified; update again when they appear, but do not wait for them – update now.
Q4. I have updated. Is there anything else to do?
- If Plex was never reachable from the Internet: updating is enough; we still recommend the exposure-reduction settings in Q7.
- If it was reachable: updating only closes the entry point and does not remove anything already installed. Complete Q5 (clean reinstall), Q6 (indicators of compromise), and Q8 (credential reset), in that order.
Q5. How do I perform a clean reinstall?
- If you would like QNAP to help confirm a compromise, first copy the Plex Logs folder (under "Plex Media Server" in the PlexData shared folder) to another location.
- Go to App Center > My Apps > Plex Media Server and select Remove.
- Use File Station to check whether a "Plex Media Server" folder still exists in the PlexData shared folder. If it does, do not reuse it: at minimum delete everything in the Codecs folder and review Preferences.xml for transcoder-related options you did not set.
- Reinstall 1.43.3 or later from App Center.
- After reinstalling, do not restore the previous contents of the Codecs folder. Plex will download the components it needs.
Q6. How do I check for indicators of compromise?
Look for any of the following:
- Unknown processes started by Plex Media Server, in particular names such as
myawesomeproxy, mylovelyminer, or x12345;
- unfamiliar
.so or .dll files in the Codecs folder;
- outbound connections to
proxystream.st;
- sustained high CPU usage while nothing is playing (see Resource Monitor);
- a Malware Remover detection (for example, detection code MR2104).
If you find any of these, do not just remove the suspicious program; other components or persistence mechanisms may remain. Complete the clean reinstall in Q5 and the credential reset in Q8. If you need QNAP's help, preserve the Logs folder first and open a case with Technical Support.
Q7. How do I reduce exposure?
- Disable Remote Access in Plex Web > Settings > Remote Access if you do not need it;
- remove the port 32400 forwarding rule on your router and disable UPnP; remove any myQNAPcloud auto router configuration for Plex;
- use a VPN (for example, QVPN Service on the NAS) when you need remote access;
- keep QTS or QuTS hero and all apps up to date, and enable Malware Remover scheduled scans and QuFirewall;
- if your device is beyond its software support period and cannot run the latest operating system, review its overall security posture as well.
Q8. Which credentials should I reset?
- Plex account: sign out all devices in your Plex account settings first, then change your Plex password. Because the administrator token may have been exposed, changing the password alone is not enough.
- NAS accounts: shared folders that Plex Media Server could access, and credentials stored on the NAS, should be treated as potentially exposed. Change the NAS administrator and user passwords, enable two-step verification, and rotate passwords or access keys stored by other services on the NAS (for example, backup jobs and cloud connections).
Q9. Will later Plex versions be published? Should I wait?
Later Plex releases will be published in App Center once verified; they contain other security fixes. Version 1.43.3 already fixes Plex2Shell, so do not wait.
Q10. How do I get help from QNAP?
Open a case with QNAP Technical Support and include your Plex version, whether Plex was reachable from the Internet, and any indicators you found. If you want QNAP to help confirm a compromise, preserve the Logs folder before removing Plex.
Further Reading
适用产品
- 运行 Plex Media Server 1.43.2 或更早版本的 QNAP NAS。
概述
Plex2Shell 指的是第三方应用程序 Plex Media Server 中的四个漏洞,影响版本1.43.2 及更早版本:CVE-2026-96652、CVE-2026-96654、CVE-2026-96655和CVE-2026-96656。每个漏洞单独存在时风险有限,但结合在一起时,允许未经身份验证的远程攻击者以 Plex Media Server 进程的权限执行任意代码。
根据 Plex 的说法,10 月 16 日发布了一个公开概念验证,未更新的面向互联网的服务器自此以来遭受了广泛攻击。被攻陷的服务器被用于运行加密货币矿机和代理软件。
修复版本Plex Media Server 1.43.3(构建 1.43.3.10861 及更高版本)已在 QNAP App Center 中提供。漏洞仅存在于 Plex Media Server 中;QNAP 操作系统如 QTS 和 QuTS hero 本身不受影响。
重要提示:如果您的 NAS 上的 Plex 在运行 1.43.2 或更早版本时可以从互联网访问,仅更新不足以解决问题。将 NAS 视为可能已被攻陷,并完成下面描述的重新安装、检查是否被攻陷以及重置凭证。
Q1. 我的 NAS 是否受到影响?
只有安装了 Plex Media Server 1.43.2 或更早版本的 NAS 受到影响。QNAP 操作系统本身不受影响,没有安装 Plex 的 NAS 无需采取任何措施。
检查版本:
- App Center > 我的应用显示1.43.3为已修补版本。
Q2. 我如何知道我的 Plex 是否可以从互联网访问?
如果在运行1.43.2 或更早版本时,任何以下情况适用,或者如果您仅在 10 月 16 日公开披露 PoC 后升级到未受影响的版本,请将 NAS 视为可能已被入侵,并完成 Q4 至 Q8:
- 在Plex Web > 设置 > 远程访问中启用了远程访问;
- 您的路由器转发端口32400;
- 您的路由器启用了 UPnP,并且启用了 Plex 远程访问(Plex 自动打开端口);
- Plex 通过 myQNAPcloud 自动路由器配置或其他方式暴露。
Q3. 我如何更新?
- 前往App Center > 我的应用 > Plex Media Server > 更新。
- 确认版本为1.43.3 或更高。
如果没有显示更新,请刷新 App Center 并确保 NAS 可以连接到互联网。
后续的 Plex 版本(包含其他安全修复)将在验证后发布;当它们出现时再次更新,但不要等待——现在就更新。
Q4. 我已经更新了。还有其他需要做的吗?
- 如果 Plex 从未能从互联网访问:更新就足够了;我们仍然建议使用 Q7 中的减少暴露设置。
- 如果可以访问:更新仅关闭入口点,并不会移除已安装的任何内容。按顺序完成Q5(清洁重装)、Q6(妥协指标)和Q8(凭证重置)。
Q5. 如何执行清洁重装?
- 如果您希望 QNAP 帮助确认妥协,首先将 Plex Logs文件夹(在PlexData共享文件夹中的“Plex Media Server”下)复制到其他位置。
- 进入App Center > 我的应用 > Plex Media Server并选择移除。
- 使用 File Station 检查在PlexData共享文件夹中是否仍然存在“Plex Media Server”文件夹。如果存在,请不要重复使用:至少删除Codecs文件夹中的所有内容,并查看Preferences.xml中您未设置的与转码器相关的选项。
- 从 App Center 重新安装1.43.3 或更高版本。
- 重新安装后,不要恢复 Codecs 文件夹的先前内容。Plex 会下载所需的组件。
Q6. 我如何检查是否存在妥协的迹象?
寻找以下任何情况:
- Plex Media Server 启动的未知进程,特别是名称如
myawesomeproxy、mylovelyminer或x12345;
.so或.dll文件在Codecs文件夹中不熟悉;- 到
proxystream.st的出站连接;
- 在没有播放任何内容时持续高 CPU 使用率(参见资源监控器);
- 恶意软件移除程序检测(例如,检测代码MR2104)。
如果发现任何这些情况,不要仅仅移除可疑程序;其他组件或持久性机制可能仍然存在。完成 Q5 中的干净重新安装和 Q8 中的凭证重置。如果需要 QNAP 的帮助,请先保留 Logs 文件夹,并与技术支持开案。
Q7. 我如何减少暴露风险?
- 如果不需要,请在Plex Web > 设置 > 远程访问中禁用远程访问;
- 移除路由器上的端口 32400 转发规则并禁用 UPnP;移除任何用于 Plex 的 myQNAPcloud 自动路由器配置;
- 当您需要远程访问时,使用 VPN(例如,NAS 上的 QVPN VPN 服务器);
- 保持 QTS 或 QuTS hero 及所有应用程序为全新状态,并启用 Malware Remover 定期扫描和 QuFirewall;
- 如果您的设备已超出软件支持期且无法运行全新操作系统,请同时检查其整体安全状况。
Q8. 我应该重置哪些凭证?
- Plex 账户:首先在您的 Plex 账户设置中注销所有设备,然后更改您的 Plex 密码。由于管理员令牌可能已被泄露,仅更改密码是不够的。
- NAS 账户:Plex Media Server 可以访问的共享文件夹和存储在 NAS 上的凭证应被视为可能已泄露。更改 NAS 的管理员和用户密码,启用两步验证,并轮换存储在 NAS 上的其他服务的密码或访问密钥(例如,备份任务和云连接)。
Q9. 后续的 Plex 版本会发布吗?我应该等待吗?
经过验证后,后续的 Plex 版本将发布在 App Center 上;它们包含其他安全修复。版本1.43.3 已经修复了 Plex2Shell,所以不必等待。
Q10. 我如何从 QNAP 获得帮助?
通过QNAP 技术支持提交一个案例,并包括您的 Plex 版本、Plex 是否可以从互联网访问以及您发现的任何指示器。如果您希望 QNAP 帮助确认是否被入侵,在移除 Plex 之前保留 Logs 文件夹。
进一步阅读


